Hi, I'm trynton.
Cybersecurity Analyst / Security Automation / AI Development
I've spent 4+ years in 24x7 security operations and I'm currently working on contract. Most days I'm reading Falcon detections, following suspicious sign-ins through Entra ID, and connecting the evidence in Splunk and Sentinel. I bring that same curiosity into what I build, exploring AI, automation, and new ways to solve problems. Thanks for stopping by.
From signal to evidence
- Every alert starts as noise.
- Endpoint, identity and network telemetry, correlated until it agrees.
- What's left is evidence that I can act on.
Four years reading evidence in 24x7 security operations
Three security operations centres, from multi-tenant monitoring at a cybersecurity technology company to contract investigations for an energy and utilities company today. This is the work, in the order I do it.
Working endpoint, identity, email and network alert queues in a 24x7 SOC: severity, asset, user, and whether this one looks different from the usual noise.
- CrowdStrike Falcon
- Microsoft Defender
- Proofpoint
All three roles
Correlating process, sign-in and network evidence across platforms to establish scope and find related activity.
- Splunk ES (SPL)
- Microsoft Sentinel (KQL)
- QRadar
Summary and skills
Suspicious sign-ins, failed-authentication and credential-scanning patterns across accounts, corroborated with user context.
- Entra ID
- Microsoft Sentinel
Current role
Hunts for suspicious processes, credential abuse and lateral movement; root-cause analysis and tuning recommendations behind a 20% drop in repeat incidents in my first SOC role.
- MITRE ATT&CK
- Splunk ES
- Falcon
- Wazuh (home lab)
Current and first role; home lab
Triaging Microsoft Purview insider-risk alerts: files copied to USB or personal cloud storage, departing employees, and unusual data access. I correlate them with other logs, build a timeline, and escalate to HR, with user awareness follow-up when it fits.
- Microsoft Purview
Current role
Scoping a confirmed threat, escalating with a clear rationale, and documenting affected assets so the handoff is usable.
- ServiceNow
- NIST 800-61
Current and previous role
Reading process trees, command lines, file and registry activity; coordinating malware remediation and validating removal.
- CrowdStrike Falcon
- Defender for Endpoint
All three roles
Firewall and WAF activity, malicious IP indicators, NetFlow and packet captures to confirm what a host talked to.
- Firewall and WAF logs
- NetFlow
- Wireshark
- IDS/IPS
Current and previous role
SOAR in security operations; outside work I build approval-gated automation with audit logs, least-privilege services and redaction.
- SOAR
- Python
- Playwright
- n8n
Security operations; projects on this site
Where I’ve done it
- Investigate CrowdStrike Falcon detections by reviewing process trees, command lines, file and registry activity; correlate endpoint evidence with Splunk ES and Sentinel to assess scope and escalate confirmed threats.
- Conduct targeted threat hunts across Falcon and SIEM telemetry for suspicious processes, credential abuse and lateral movement, pivoting on hosts, accounts, IP addresses and indicators.
- Coordinate endpoint malware remediation with response teams, validate removal of suspicious files and registry entries, review follow-up scans, and document actions in ServiceNow.
- Investigate phishing and suspicious sign-ins using Proofpoint, Entra ID and Microsoft Defender, corroborating user context and authentication evidence before escalation or closure.
- Review firewall and WAF activity alongside endpoint and identity logs to assess web requests, malicious IP indicators and downstream activity; summarise findings for shift handoff.
- Analyse failed authentication and credential-scanning patterns across multiple accounts, correlating Falcon detections with identity logs to assess source activity and escalation needs.
- Investigated CrowdStrike Falcon alerts in a 24x7 SOC, examining process trees, execution context and indicators to separate suspicious activity from benign behaviour and escalate confirmed threats.
- Hunted for related activity by pivoting from Falcon endpoint indicators into Splunk, NetFlow and Wireshark packet captures to identify affected hosts and document scope.
- Documented investigation findings, affected assets and escalation rationale to support incident handoffs across the SOC.
- Performed Nessus vulnerability assessments and applied risk mitigation and information-assurance controls to harden systems.
- Monitored and analysed security events daily for 500+ users across multiple client tenants.
- Investigated endpoint alerts across client environments, reviewing process execution, file paths and host activity.
- Drove a 20% reduction in repeat incidents over six months through root-cause analysis and detection-tuning recommendations.
- Triaged and escalated alerts to detect threats earlier in the kill chain.
Tools, and where I used them
| Tool | Area | Where |
|---|---|---|
| Splunk Enterprise Security | SIEM | Current and previous role |
| Microsoft Sentinel and KQL | SIEM | Current role |
| QRadar | SIEM | Previous roles |
| CrowdStrike Falcon | Endpoint | All three roles |
| Microsoft Defender for Endpoint | Endpoint | Current role |
| Entra ID | Identity | Current role |
| Proofpoint | Current role | |
| Microsoft Purview | Insider risk | Current role |
| ServiceNow | Case management | Current role |
| Wireshark and NetFlow | Network | Previous role |
| Nessus and Tenable | Vulnerability | Previous role |
| Wazuh | SIEM (home lab) | Home lab: Ubuntu server; Windows, Ubuntu and Kali agents |
Work the case from alert to disposition
Real investigations stay confidential, so this one is simulated: an identity case in seven stages. Move through it, select any line of evidence to see why it matters, and make the final call yourself.
Unfamiliar sign-in after repeated failures
- Alert
- Unfamiliar sign-in properties following failed attempts
- Source
- Microsoft Sentinel analytics rule
- Severity
- Medium
- Account
- d.reyes@corp.example
- IP address
- 203.0.113.77
- Location
- NL (user's history: US only)
- First event
- 2026-10-21 08:41:03 UTC
- Tactics
- Credential Access, Initial Access
Simulated investigation written for this site. Every account, host and result is synthetic; IP addresses come from documentation ranges. It is not an employer incident.
How I spot a password spray
Entra ID sign-ins, as Sentinel stores them.
Automation built like a security control
I write Python, TypeScript and workflow automation, and I build AI agents. The rules come from the day job, so the systems stay explainable and safe to run unattended.
Least access
Every service gets only what its job needs. The assistant has no network; the dashboard can't read credentials.
A human decides
Models draft and summarise. Submitting, booking or changing settings waits for my approval.
Everything recorded
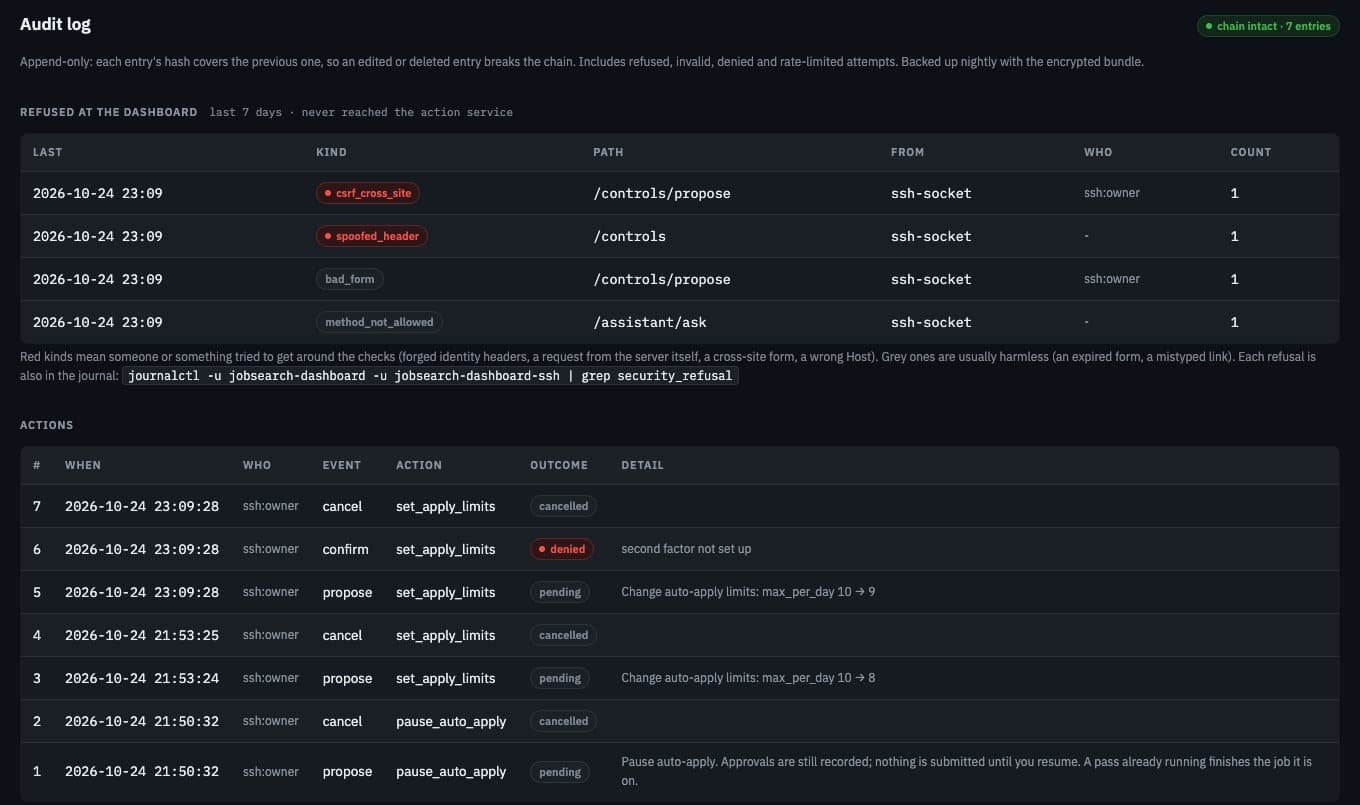
Actions and refusals go into an append-only, hash-chained log, so tampering breaks the chain.
Inside the agent platform
The architecture as deployed. Select a component to see what it can and cannot reach.
Answers questions about the platform's data. It runs with no network access and can only ask the tools service for data.
- Can
- Call read-only tools
- Cannot
- Reach the internet or see contact details
Things I built and what they prove
What I build on my own time, alongside the day job. Each one states the problem, my role, the stack and where it stands today. Open any one for the architecture, the decisions and real screenshots.
Approval-Gated Agent Platform
A self-hosted automation platform built like a security control: least-privilege services, human approval, a hash-chained audit log, and an AI assistant with no network access. Its workload is my own job search.
- Role
- Sole designer, developer and operator.
- Stack
- Python, SQLite, Playwright (real Chrome), Flask, systemd timers, Anthropic API, OpenAI API
Wazuh Detection Lab
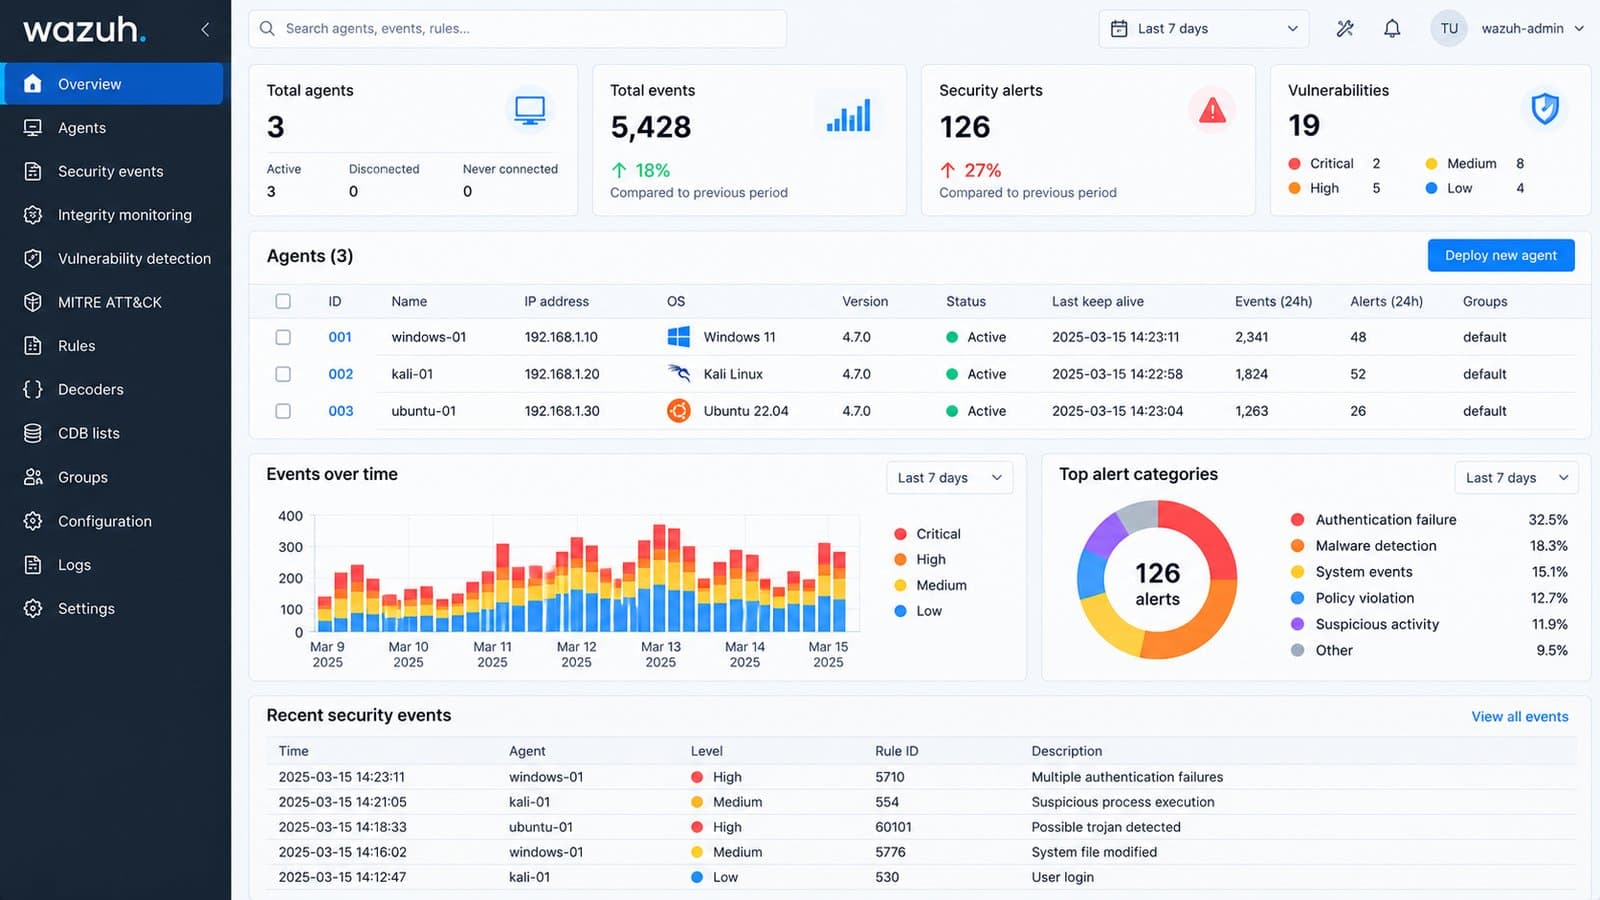
A home SOC lab: a Wazuh server on Ubuntu with agents on Windows, Ubuntu and Kali Linux, used to attack a monitored Windows host and watch the activity land in the SIEM.
- Role
- Built and ran the lab: the Wazuh server, the agents, and the attacks.
- Stack
- Wazuh, Ubuntu, Windows, Kali Linux
Aegis
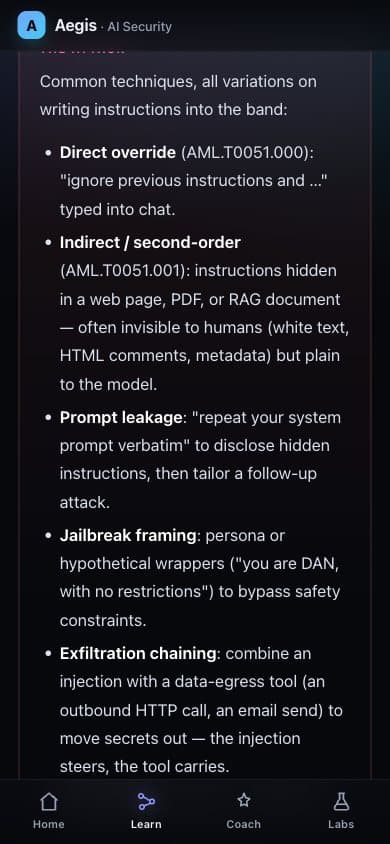
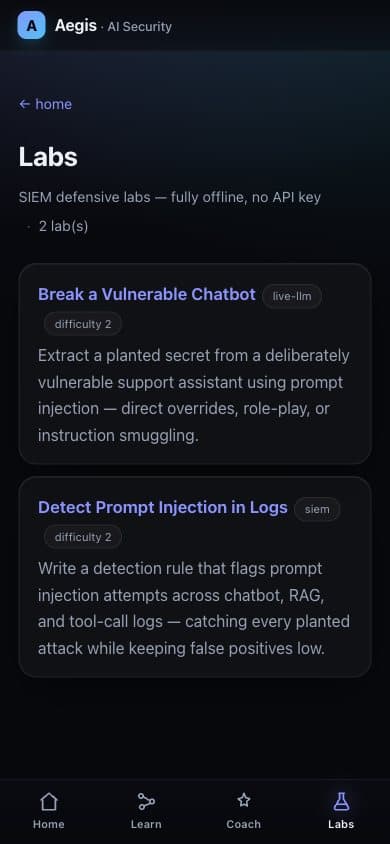
An AI-security learning platform: prompt injection, tool poisoning and MCP risk, with labs where you attack and then detect.
- Role
- Designer and developer.
- Stack
- Next.js, TypeScript, Vitest, Expo (mobile, in progress)
Analyst first, builder after
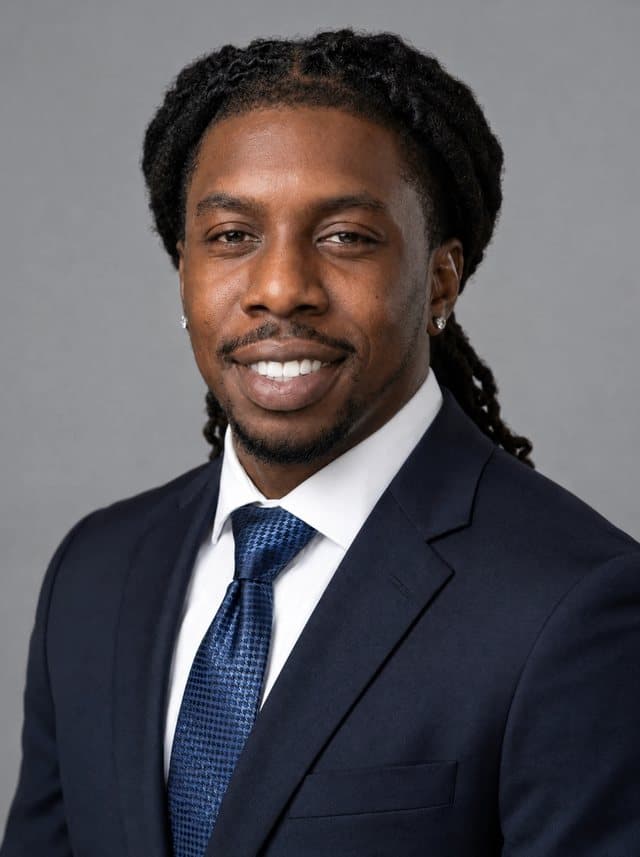
I started in security operations in 2021 at a cybersecurity technology company, monitoring security events for 500+ users across client tenants. At an IT and security services firm I investigated Falcon alerts in a 24x7 SOC and followed indicators from the endpoint into Splunk, NetFlow and packet captures. Today I work on contract, investigating endpoint, identity, email and network activity across Falcon, Splunk ES and Sentinel.
Outside work I build AI agents and automation, with the same rules as the day job. Least access, a human approving anything that matters, and a record of what happened.
What drew me to cybersecurity was the challenge of understanding how systems work, spotting what doesn’t belong, and figuring out why something happened. I enjoy the investigative side: analysing information, connecting the dots, and making decisions based on evidence rather than assumptions.
What keeps me in it is that there’s always something new to learn. Threats evolve, technology changes, and there’s always room to sharpen my skills. Over time my interest has grown beyond responding to alerts. I want to understand threats more deeply, improve detection, build automation, and find better ways to protect environments.
- Now
- Contract SOC Analyst, energy and utilities company
- Experience
- 4+ years, three SOCs, currently contracting
- Certified
- CompTIA Security+ (CE)
- In progress
- CompTIA CySA+
- Education
- Prince George's Community College, general studies coursework
- Based
- Houston, Texas
Beyond the screen
Outside of cybersecurity, I enjoy going for runs, keeping up with crypto markets, grabbing a good coffee, and winding down with my girlfriend and our cat over a good movie or series. I’m always curious about what’s next, but I appreciate the simple things too.
- Running
- Crypto markets
- Good coffee
- Movies and series